In brief
European authorities have warned that refrigeration units across the bloc are under a new wave of cyber threats, urging organisations to take immediate steps to reduce exposure. The alert, issued by ENISA, the European Commission, Europol’s EC3, the EU CSIRTs Network and EU‑CyCLONe, stresses the importance of the NIS2 Directive and the new EU Cyber Resilience Act for secure design and incident reporting. Organisations are urged to consult national cyber‑security advisories and to prepare for the Act’s secure‑by‑design requirements set for December 2027.
On 5 November, European Union cybersecurity authorities issued an urgent alert following a new wave of incidents targeting refrigeration systems that unfolded on 1 and 2 November across several member states.
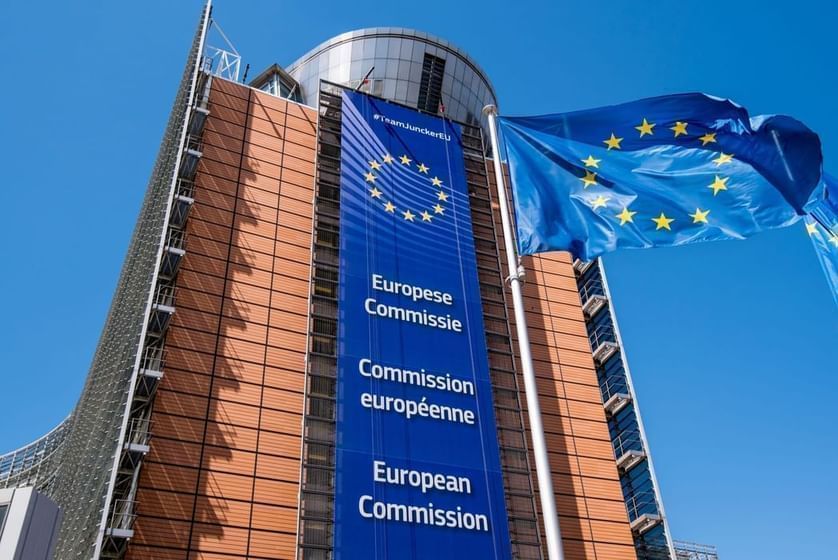
The warning was issued jointly by the European Union Agency for Cybersecurity (ENISA), the European Commission, Europol’s European Cybercrime Centre (EC3), the EU Computer Security Incident Response Teams Network (EU CSIRTs Network) and the European Cyber Crisis Liaison Organisation Network (EU‑CyCLONe).
National cybersecurity response teams and crisis management authorities are currently investigating the incidents and are exchanging information while monitoring developments in real‑time.
In its advisory, ENISA urged organisations to consult the latest security advisories issued by national cyber‑security response teams, which are available through official channels and ENISA’s advisory collection.
Organisations are also reminded that manufacturers, under the EU Cyber Resilience Act, have been required since 11 September 2026 to report severe incidents and actively exploited vulnerabilities through the Act’s Single Reporting Platform.
According to the Act, the main cybersecurity requirements will take effect on 11 December 2027. These requirements mandate manufacturers to incorporate security into product design, provide security support throughout product lifecycles and address vulnerabilities without delay.
Those organisations covered by the EU’s Network and Information Security Directive (NIS2) must also implement cybersecurity risk management measures and report significant incidents to the relevant national authorities or computer security incident response teams.
ENISA has repeatedly promoted secure‑by‑design and secure‑by‑default principles through technical advisories, guidance and information‑sharing initiatives aimed at strengthening cybersecurity across the EU.
Context and Implications
The new wave of attacks highlights the expanding threat landscape toward industrial and critical infrastructure, with refrigeration systems—central to food safety and supply chains—identified as a vulnerable target.
Regulatory bodies argue that the NIS2 Directive already requires organisations that run essential services, including refrigeration equipment for food storage, to adopt robust cyber‑risk management and incident reporting frameworks.
With the EU Cyber Resilience Act coming into force next year, manufacturers of such systems will face stricter design standards and mandatory reporting of serious incidents, which are expected to reduce overall exposure to cyber‑threats.
Given the rapidly evolving nature of cyber‑attacks, these coordinated EU actions aim to close gaps that allow attackers to compromise cooling networks, potentially leading to spoilage of perishables or disruption of large‑scale logistics.
Open Questions and Next Steps
Key questions remain about the specific methods used by attackers, whether the incidents involved insider threats or external hacking attempts, and how the breaches were contained.
The joint statement from ENISA, the European Commission and its partners emphasizes ongoing monitoring but does not yet disclose technical details of the attacks.
National cybersecurity authorities are continuing investigations and are expected to release more comprehensive guidance as understanding of the threat evolves.
Stakeholders in the refrigeration industry are urged to review their risk‑management practices, update protective measures, and ensure alignment with NIS2 and forthcoming Act requirements ahead of the deadline.
Overall, the EU’s coordinated response, centred on immediate action and future regulatory compliance, underscores an effort to safeguard essential refrigeration infrastructure from emerging cyber‑threats, while prompting organisations to prepare for the upcoming shift toward secure‑by‑design product standards.